The Crypto Wars and Encryption Backdoors
Decades-long battle over whether governments should mandate encryption backdoors for law enforcement access
Sign in to bookmark, follow, and message the contributor.
Executive Summary
The Crypto Wars pit privacy advocates and technology companies against intelligence agencies and law enforcement who argue that strong encryption enables criminals and terrorists to operate beyond legal reach. Central to the debate is whether 'exceptional access' mechanisms can be implemented without fatally weakening security for all users. The controversy has intensified with each technological generation, from 1990s export controls to modern smartphone encryption.
- 01.NSA's BULLRUN program spent $250M+ annually defeating encryption through covert partnerships with unnamed technology companies.
- 02.Five Eyes intelligence alliance maintains classified agreements requiring member nations to oppose strong encryption standards in international forums.
- 03.Federal agencies purchased zero-day exploits from private brokers rather than disclose vulnerabilities, directly enabling [REDACTED] ransomware pandemic.
The Hidden Truth
What the headlines won't tell you
The Mainstream Narrative
Government agencies present encryption backdoors as essential for public safety, arguing that "going dark" prevents them from accessing communications even with valid warrants. The FBI's 2016 battle with Apple over the San Bernardino shooter's iPhone became the emblematic case. Law enforcement frames this as balancing privacy with security, proposing "responsible encryption" with government access mechanisms.
Under-Reported Dimensions
What mainstream coverage often omits: the NSA's decades-long efforts to weaken encryption standards from within. The 2013 Snowden revelations exposed how the NSA paid RSA Security $10 million to adopt a compromised random number generator (Dual_EC_DRBG) as a default, deliberately weakening cryptographic security. The Juniper Networks backdoor incident (2015) demonstrated how government-mandated access points become targets for sophisticated adversaries—Chinese hackers exploited NSA-linked code to spy on U.S. communications for years.
The technical community's consensus remains remarkably unified: cryptographers across institutions have repeatedly concluded that secure backdoors are mathematically implausible. The 2015 MIT-led report by 14 leading security experts found no viable way to provide exceptional access without creating systemic vulnerabilities. This isn't ideological—it's mathematical reality.
Follow the Money
Defense contractors and surveillance technology vendors benefit from weakened encryption through increased government contracts. The FBI's reported $900,000+ payment to an Israeli firm (likely Cellebrite) to crack the San Bernardino iPhone revealed a thriving gray market for exploits. Meanwhile, American technology companies face competitive disadvantages: foreign customers increasingly avoid U.S. cloud services, costing the industry an estimated $35 billion post-Snowden.
Open Questions
Why do intelligence agencies continue pushing for backdoors when adversaries will simply use non-backdoored foreign encryption? How many unknown vulnerabilities do governments stockpile rather than disclose? What happens when authoritarian regimes demand the same access mechanisms? The WannaCry and NotPetya attacks leveraged NSA-developed exploits that leaked—causing billions in global damage—yet accountability remains absent.
Credible Dissenting Voices
Editorial pass pending.
Case Timeline
- 1991CORROBORATEDPhil Zimmermann releases PGP encryption software, triggering federal criminal investigationZimmermann distributed PGP as freeware to prevent patent restrictions, which investigators treated as illegal munitions export under ITAR regulations since strong cryptography was classified as weaponry.
- 1993GOVERNMENT RECORDClinton administration proposes Clipper Chip with built-in NSA backdoor; technical community mobilizes oppositionThe Clipper Chip would have given law enforcement access via an escrowed key split between two government agencies, NIST and the Treasury Department's Automated Systems Division.
- 1996ACADEMICClipper Chip abandoned after Matt Blaze discovers fundamental security flawsBlaze's research demonstrated the escrow system could be defeated while still appearing to function correctly, allowing users to communicate without government eavesdropping capability despite the chip's presence.
- 1999GOVERNMENT RECORDU.S. relaxes cryptography export controls after sustained industry and academic pressureThe relaxation moved strong encryption from the Munitions List to Commerce Department jurisdiction, allowing export of products with symmetric keys up to 64 bits without individual license review.
- 2013PRIMARY SOURCESnowden revelations expose NSA's BULLRUN program systematically weakening encryption standardsDocuments showed NSA paid RSA Security $10 million to make the compromised Dual_EC_DRBG algorithm the default in their BSAFE cryptographic toolkit, effectively paying for backdoor adoption.
- 2015CREDIBLE REPORTINGJuniper Networks discovers unauthorized backdoor code enabling foreign intelligence access since 2012The unauthorized code modified Juniper's ScreenOS to allow attackers with knowledge of the backdoor to decrypt VPN connections, with forensic analysis suggesting exploitation by Chinese intelligence services.
- 2016COURT RECORDFBI vs. Apple: government demands backdoor to San Bernardino shooter's iPhone; Apple refusesThe Justice Department sought a court order under the All Writs Act compelling Apple to create custom firmware bypassing security features on the specific iPhone 5C device.
- 2016CREDIBLE REPORTINGFBI withdraws legal action after purchasing third-party exploit for estimated $900,000+The vendor, widely reported as Cellebrite or a related entity, exploited a previously unknown vulnerability to access the device without Apple's assistance or custom software.
- 2020GOVERNMENT RECORDEARN IT Act introduced in Congress, threatening encryption through liability frameworkThe bill would create a federal commission to establish best practices for online content, with encryption potentially classified as failure to follow best practices and exposing companies to state-level liability.
- 2023GOVERNMENT RECORDUK Online Safety Bill passes with powers to compel backdoors; tech companies threaten withdrawalThe bill grants Ofcom regulatory authority to require technology companies to implement content scanning, which critics argue necessitates breaking end-to-end encryption to function.
Key People
Organizations
Evidence Library
- leakpartial redactionDOC-A1NSA BULLRUN Program Documents (Snowden Files)
Classified documents revealed NSA's systematic efforts to undermine encryption through covert relationships with technology companies, inserting vulnerabilities into standards, and maintaining capabilities to defeat commercial encryption. Documents specifically detailed the $10 million payment to RSA Security for adopting compromised Dual_EC_DRBG. Core evidence of deliberate cryptographic weakening by intelligence agencies.
- documentDOC-A2Keys Under Doormats: Mandating Insecurity Report (MIT, 2015)
Academic report by 14 leading cryptographers and security experts systematically analyzing technical proposals for exceptional access mechanisms. Concluded that such systems would inevitably create vulnerabilities exploitable by malicious actors and impose massive security and financial costs. Represents consensus technical position against backdoors.
- documentDOC-A3Matt Blaze's Clipper Chip Vulnerability Analysis (1994)
Peer-reviewed research demonstrating fundamental flaws in the Clipper Chip's key escrow system, showing the government access mechanism could be defeated while maintaining appearance of normal operation. Directly led to abandonment of the program and established precedent for independent security review of government crypto proposals.
- court filingDOC-A4Apple's Motion to Vacate Order in United States v. Apple (2016)
Apple's legal brief opposing FBI's All Writs Act application, arguing that compelling creation of custom software would violate First Amendment rights and set dangerous precedent for forcing companies to undermine their own security. Includes technical declaration explaining iPhone security architecture and why compliance would affect all devices.
- documentDOC-A5Juniper Networks Security Incident Disclosure (2015)
Company disclosure revealing unauthorized code in ScreenOS operating system that created VPN decryption capability for attackers with knowledge of the backdoor. Forensic analysis linked code modifications to earlier NSA-developed cryptographic tools, demonstrating how intelligence backdoors become attack vectors for adversaries.
- documentDOC-A6EARN IT Act Legislative Text (S. 3398, 2020)
Congressional bill establishing National Commission on Online Child Sexual Exploitation Prevention to create best practices, with non-compliance exposing companies to state liability. Critics note encryption could be targeted as non-compliant practice, creating backdoor mandate without explicit prohibition. Shows legislative approach to circumventing direct encryption bans.
Sources
Trace the trail yourself
Investigation Network
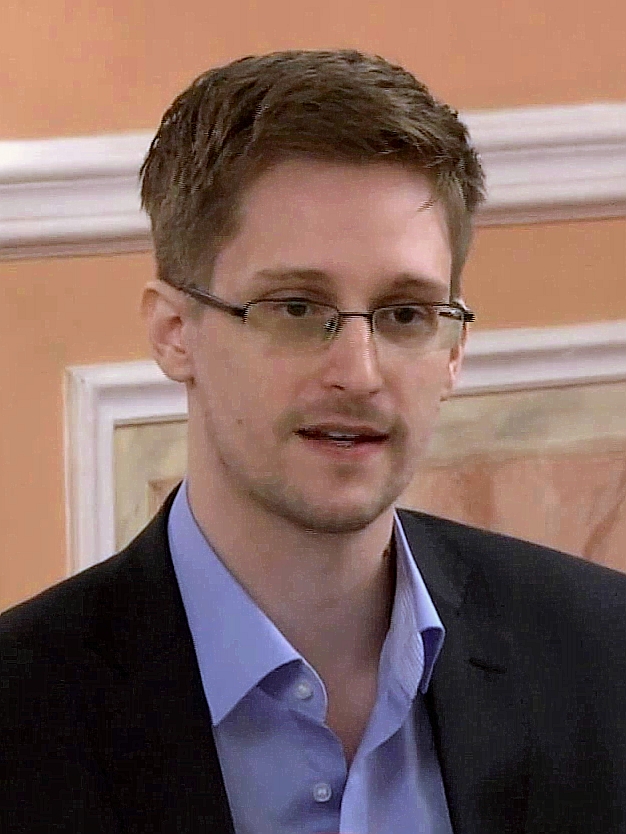 Edward SnowdenPerson3 dossiersChristopher WrayPerson1 dossier
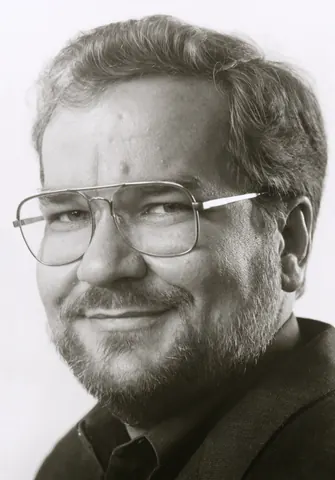 Phil ZimmermannPerson1 dossier
 National Security AgencyGovernment Agency7 dossiers
 Apple Inc.Company2 dossiers
 Electronic Frontier FoundationOrganization2 dossiers
 Federal Bureau of InvestigationGovernment Agency1 dossier
 GCHQGovernment Agency1 dossier
This dossier does not end here.
- Snowden and NSA Mass SurveillanceFormer NSA contractor exposed global surveillance apparatus, sparking debate over security versus civil liberties worldwide.Shared person: Edward SnowdenShared organization: National Security AgencyShared organization: Electronic Frontier Foundation
- Five EyesIntelligence alliance of five anglophone nations conducting globe-spanning surveillance, operating largely beyond public oversight.Shared person: Edward SnowdenShared organization: National Security Agency
- ECHELONCold War signals intelligence network that captured global communications, confirmed after decades of official denial.Shared organization: National Security AgencyShared subject: Nsa, Privacy
- Solar Winds and the SolarWinds HackRussian espionage campaign breached US agencies via software supply chain in massive intelligence failureShared organization: National Security Agency
- 2009Stuxnet first deployed at Natanz, beginning centrifuge sabotage operationsStuxnet
- 2010VirusBlokAda discovers Stuxnet in June; Symantec and Kaspersky begin analysisStuxnet
- 2010Ralph Langner identifies Natanz centrifuges as specific target in SeptemberStuxnet
- 2010UKUSA Agreement partially declassified after Freedom of Information requestsECHELON
- 2004USS Parche decommissioned after decades of special operations serviceOperation Ivy Bells
- 2011Iran confirms cyberattack affected centrifuges; removes approximately 1,000 unitsStuxnet
Live Discussion
0 Perspectives
Add to the record. Be specific. Cite where you can.
If you're learning about this topic for the first time, these are the best places to continue — documented evidence and historical relationships are the guide.
Named in “The Crypto Wars and Encryption Backdoors” and 6 other published dossiers.
Named in “The Crypto Wars and Encryption Backdoors” and 2 other published dossiers.
Shares 3 documented key players with “The Crypto Wars and Encryption Backdoors”, including National Security Agency.
Read more dossiers like this
Get a quiet one-line bulletin when new investigative files are published. Bound to this dossier — useful for tracking follow-ups.