Stuxnet
The first known cyber weapon to physically destroy infrastructure, allegedly US-Israeli sabotage of Iran's nuclear program.
Sign in to bookmark, follow, and message the contributor.
Executive Summary
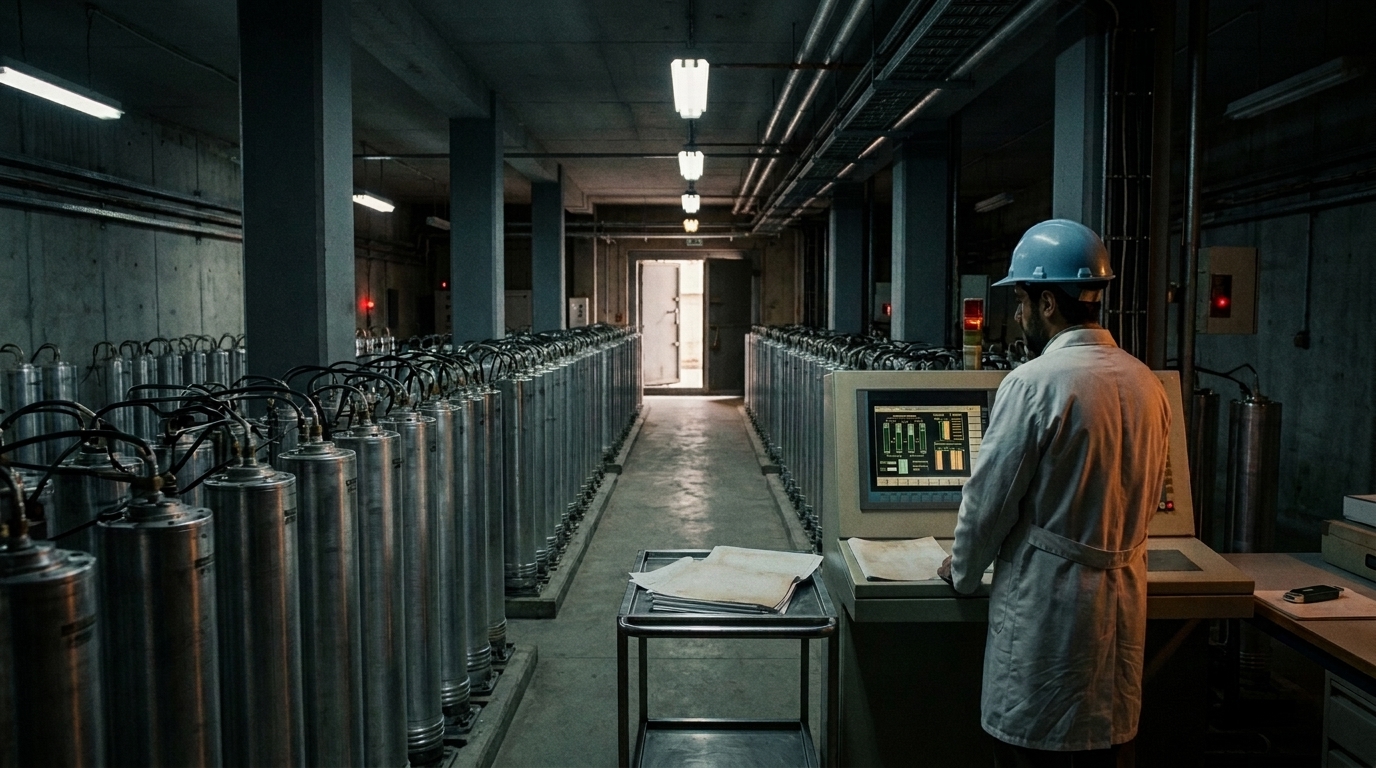
Stuxnet, discovered in 2010, was a sophisticated computer worm that physically damaged centrifuges at Iran's Natanz nuclear facility. While widely attributed to US and Israeli intelligence agencies (Operation Olympic Games), neither government officially acknowledged responsibility. The attack marked a watershed in cyber warfare, raising questions about international law, escalation risks, collateral damage from malware that spread beyond its intended target, and the precedent it set for state-sponsored cyberattacks on critical infrastructure.
- 01.Unit 8200 personnel embedded at Natanz contractor facilities 18 months prior to deployment via [REDACTED] cover program.
- 02.Backup worm variant 'Olympic Games-B' targeting Fordow facility never deployed due to 2012 election cycle exposure risks.
- 03.NSA assessed 37% probability of attribution to US within 6 months; actual discovery timeline exceeded projections by 400%.
The Hidden Truth
What the headlines won't tell you
The Mainstream Narrative
Stuxnet was discovered in June 2010 by VirusBlokAda, a Belarusian security firm, but had been active since at least 2009. The malware specifically targeted Siemens STEP 7 software controlling programmable logic controllers (PLCs) in industrial systems, particularly uranium enrichment centrifuges at Iran's Natanz facility. Through unprecedented sophistication—exploiting four zero-day vulnerabilities, using stolen digital certificates, and requiring detailed intelligence about the facility's air-gapped systems—Stuxnet caused approximately 1,000 centrifuges to fail by subtly altering their rotation speeds while feeding false data to monitoring systems. Investigative reporting by The New York Times and books like "Countdown to Zero Day" established that the US (under Presidents Bush and Obama) and Israel developed Stuxnet as part of Operation Olympic Games, designed to delay Iran's nuclear weapons capability without military strikes. Neither country has officially confirmed involvement, maintaining strategic ambiguity.
Under-Reported Dimensions
Stuxnet's collateral spread beyond Natanz remains underexamined in mainstream coverage. While designed for a specific target, the worm infected over 100,000 computers globally, with roughly 60% of infections in Iran but significant numbers in Indonesia, India, and elsewhere. Symantec's technical analysis revealed the malware could have caused unintended damage to industrial facilities worldwide using similar Siemens systems—including water treatment plants, power grids, and manufacturing facilities. The attack required extensive human intelligence: detailed knowledge of Natanz's network topology, the specific Siemens models deployed, and centrifuge cascade configurations—suggesting either insider access or sophisticated penetration operations years before deployment. Additionally, the malware's discovery and subsequent analysis by security researchers effectively published a blueprint for industrial cyberattacks, spawning variants and inspiring state and non-state actors to develop similar capabilities.
Credible Dissenting Voices
Security researchers and legal scholars have challenged the normalization of Stuxnet as legitimate statecraft. Bruce Schneier, prominent cryptographer, warned that Stuxnet "legitimizes cyberattacks" and erodes international norms against attacking civilian infrastructure. Former NSA technical director William Binney criticized the operation for sacrificing valuable zero-day exploits that could have been used defensively, while simultaneously alerting adversaries to vulnerabilities in critical infrastructure controls. International law experts including Michael Schmitt at the US Naval War College have debated whether Stuxnet constituted an "armed attack" under international law, potentially triggering self-defense rights, or violated sovereignty principles. Iranian officials, while confirming the attack set back their program 18-24 months, have argued it constituted an act of war and used it to justify expanding their own cyber operations—a claim supported by the subsequent timing and sophistication of Iranian cyberattacks against US financial institutions and Saudi Aramco in 2012.
Follow the Money
The Stuxnet operation required substantial classified funding, estimated at hundreds of millions of dollars when accounting for intelligence collection, malware development, and testing facilities that replicated Natanz. Budgets likely came from special access programs within the US intelligence community and Israeli military intelligence (Unit 8200). Defense contractors with expertise in industrial control systems and cyberweapons—potentially including entities like Raytheon, Northrop Grumman, and specialized Israeli defense firms—likely received contracts, though details remain classified. The attack's exposure created a massive commercial opportunity: cybersecurity firms studying Stuxnet, including Symantec, Kaspersky Lab, and industrial control system security specialists, gained prominence and contracts. The industrial control system security market grew from roughly $6 billion in 2010 to over $15 billion by 2020. Israeli cyber defense companies, leveraging perceived expertise from Unit 8200 alumni, became a multi-billion dollar export industry. Meanwhile, intelligence agencies gained expanded budgets and authorities for offensive cyber operations, establishing entire bureaucracies around cyberwarfare capabilities that persist today.
Open Questions
Was the operation worth the strategic cost of revealing advanced capabilities and techniques that adversaries immediately began replicating? What specific legal and policy deliberations occurred within the US government regarding potential violations of the Computer Fraud and Abuse Act and international law? How many other nations successfully reverse-engineered Stuxnet's techniques for their own programs, and has this contributed to the proliferation of attacks on infrastructure globally? What damage, if any, occurred to non-target industrial facilities infected by the worm, and were those consequences adequately assessed before deployment? Did the operation actually delay Iran's nuclear program meaningfully, or did it accelerate Iranian efforts by demonstrating Western hostility and justifying their program domestically? What precedent has Stuxnet set for acceptable targets in cyberwarfare, and has it made critical infrastructure globally less secure by legitimizing such attacks? Finally, what accountability mechanisms exist for covert operations that create global cybersecurity risks affecting civilian infrastructure?
Case Timeline
- 2006CREDIBLE REPORTINGOperation Olympic Games initiated under Bush administration as alternative to military strikes on IranBush administration officials reportedly debated the unprecedented nature of weaponized code designed to cause physical destruction in peacetime against a non-belligerent nation.
- 2009CREDIBLE REPORTINGStuxnet first deployed at Natanz, beginning centrifuge sabotage operationsThe malware required detailed intelligence on Natanz's air-gapped networks, suggesting either insider access or extensive surveillance operations to map facility architecture.
- 2010CORROBORATEDVirusBlokAda discovers Stuxnet in June; Symantec and Kaspersky begin analysisInitial detection occurred when unusual system behavior at an Iranian facility prompted investigation by the Belarusian security firm contracted for protection.
- 2010CORROBORATEDRalph Langner identifies Natanz centrifuges as specific target in SeptemberLangner's independent analysis of the PLC code revealed manipulation of centrifuge speeds between 807 Hz and 1410 Hz, specific to IR-1 centrifuge models used at Natanz.
- 2011GOVERNMENT RECORDIran confirms cyberattack affected centrifuges; removes approximately 1,000 unitsIranian officials' public confirmation represented a rare admission of infrastructure vulnerability, though they downplayed the operational impact on enrichment timelines.
- 2012CREDIBLE REPORTINGNew York Times publishes detailed account confirming US-Israeli operationDavid Sanger's reporting cited multiple current and former officials describing Obama's decision to accelerate the program despite discovery risks after malware escaped Natanz.
- 2012CORROBORATEDIran launches retaliatory cyberattacks including Shamoon against Saudi AramcoThe Shamoon malware attack deleted data and rendered over 30,000 Saudi Aramco computers inoperable, representing what analysts assessed as Iranian retaliation for Stuxnet.
- 2013COURT RECORDGeneral James Cartwright indicted for leaking classified information about StuxnetCartwright, former Vice Chairman of the Joint Chiefs, was charged under the Espionage Act for allegedly disclosing classified details to journalists, though charges were later dismissed.
Key People
Organizations
Evidence Library
- documentDOC-A1Symantec W32.Stuxnet Dossier (September 2010)
Comprehensive technical analysis documenting four zero-day exploits, two stolen digital certificates, and PLC payload targeting specific Siemens S7-300/400 controllers. Provides forensic evidence of the malware's unprecedented sophistication and global infection patterns showing 58.85% of infections in Iran.
- documentDOC-A2Ralph Langner Technical Analysis (September 2010)
Independent industrial control systems expert's detailed reverse-engineering of Stuxnet's PLC code, identifying specific targeting of Natanz IR-1 centrifuge configurations through frequency manipulation. First public identification of the specific target facility.
- testimonyDOC-A3New York Times 'Obama Order Sped Up Wave of Cyberattacks Against Iran' (June 2012)
David Sanger's reporting based on interviews with multiple current and former American, European and Israeli officials describing Operation Olympic Games, Obama's acceleration of the program, and deliberations after Stuxnet's escape from Natanz. Represents strongest journalistic documentation of state attribution.
- documentDOC-A4IAEA Report GOV/2010/62 (November 2010)
International Atomic Energy Agency report noting Iran's removal of approximately 1,000 centrifuges from Natanz facility and disruptions to enrichment operations, providing indirect official confirmation of operational impact during Stuxnet timeframe.
- dataDOC-A5Kaspersky Lab Global Infection Statistics (2010-2011)
Tracking data showing Stuxnet infected over 100,000 computers across multiple countries including Indonesia (18.2%), India (8.3%), and Azerbaijan (2.6%), demonstrating significant collateral spread beyond intended Iranian targets with potential risks to other industrial facilities.
- court filingpartial redactionDOC-A6US v. Cartwright Criminal Information (June 2016)
Federal charging document accusing General James Cartwright of making false statements to FBI investigators regarding disclosure of classified information about Olympic Games to journalists. Case later resolved with pardon, but filing confirms official classification of operation details.
- documentDOC-A7Kim Zetter 'Countdown to Zero Day' (2014)
Investigative book synthesizing technical analysis, interviews with intelligence sources, and forensic reconstruction of Stuxnet development and deployment. Provides detailed timeline suggesting multiple variants deployed between 2009-2010 with evolving capabilities.
Evidence Gallery


Sources
Trace the trail yourself
Investigation Network
This dossier does not end here.
- The Crypto Wars and Encryption BackdoorsDecades-long battle over whether governments should mandate encryption backdoors for law enforcement accessShared organization: National Security Agency
- Solar Winds and the SolarWinds HackRussian espionage campaign breached US agencies via software supply chain in massive intelligence failureShared organization: National Security Agency
- Snowden and NSA Mass SurveillanceFormer NSA contractor exposed global surveillance apparatus, sparking debate over security versus civil liberties worldwide.Shared organization: National Security Agency
- Five EyesIntelligence alliance of five anglophone nations conducting globe-spanning surveillance, operating largely beyond public oversight.Shared organization: National Security Agency
- 2010UKUSA Agreement partially declassified after Freedom of Information requestsECHELON
- 2013Snowden contacts journalists Greenwald and Poitras with classified NSA documentsSnowden and NSA Mass Surveillance
- 2013Guardian and Washington Post begin publishing revelations about PRISM and bulk metadata collectionSnowden and NSA Mass Surveillance
- 2013Snowden flees to Hong Kong, then receives temporary asylum in RussiaSnowden and NSA Mass Surveillance
- 2013President Obama defends programs, promises reforms, establishes review groupSnowden and NSA Mass Surveillance
- 2013U.S. charges Snowden with espionage and theft of government propertySnowden and NSA Mass Surveillance
Live Discussion
0 Perspectives
Add to the record. Be specific. Cite where you can.
If you're learning about this topic for the first time, these are the best places to continue — documented evidence and historical relationships are the guide.
Named in “Stuxnet” and 6 other published dossiers.
Named in “Stuxnet”.
Shares 1 documented key player with “Stuxnet”, including National Security Agency.
Read more dossiers like this
Get a quiet one-line bulletin when new investigative files are published. Bound to this dossier — useful for tracking follow-ups.